Our review of metamaskwallet.to found a wallet guide that used the MetaMask name and a security report that flagged the exact address for phishing. Readers looking for the wallet should start at MetaMask’s own download page. The warning gives readers reason to avoid the address. Its operator remains unidentified.
What the Homepage Looked Like
A February 21, 2026 browser capture shows the name MetaMask above a short guide to Web3, decentralized finance and NFTs. Across the top, the reader could see separate navigation labels for an extension, a login, a wallet, a download and an app. In the captured viewport, the space below those links contains explanatory text, a promotional graphic and a video preview.
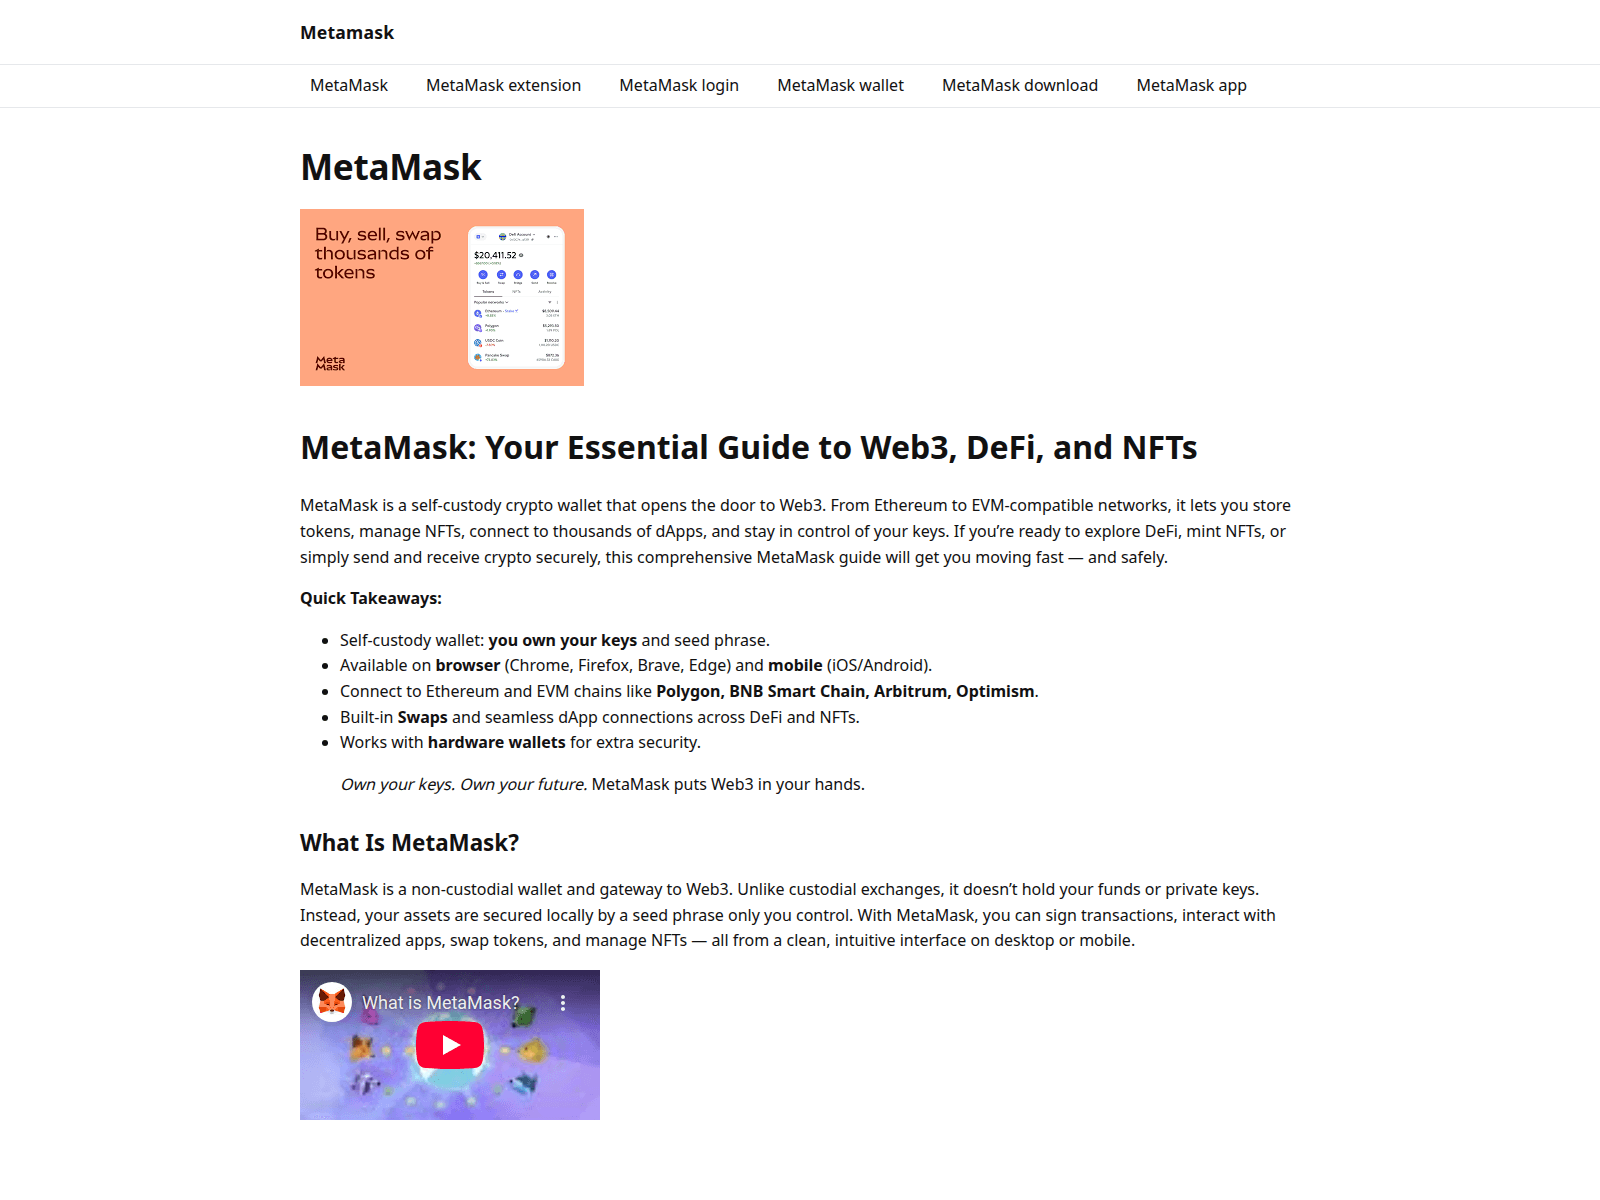

The indexed homepage text offered practical advice about installing a browser extension and backing up a wallet. It told readers to use an official source and warned them against typing a recovery phrase into a website. That advice is worth distinguishing from the identity of the publisher. Anyone can reproduce wallet instructions, including accurate ones, on a domain they control.
A reader searching for a wallet login could see a familiar label. For a visitor seeking access, the screenshot does not establish where the link led, who controlled the destination, or whether clicking it opened an extension.
Why Security Researchers Flagged Metamaskwallet.to
PhishDestroy published an exact-domain assessment classifying the site as MetaMask phishing. It records first detecting the address on February 21 and gives March 11, 2026 as the date of its high-risk classification. The page also identifies a URLScan browser capture. The guide title in that record matches the subject and branding visible in the archived image. Read the PhishDestroy domain report.
PhishDestroy aggregates dated results from several services. Counting each entry on its page as a separate firsthand investigation would overstate our review. We verified the report and inspected the image it cites. We did not observe a recovery phrase being submitted or a transaction being signed.
A screenshot can tie a page design to a particular address and date. Establishing that a visitor lost funds would require evidence of what the visitor did next and which transaction followed. We did not identify a documented loss with that chain of evidence in the materials reviewed.
Where MetaMask Sends Readers for Installation
MetaMask publishes installation instructions on its own download page, where readers can choose a mobile app or browser extension. Its instructions direct extension users to their browser’s store. For mobile users, MetaMask warns about cloned apps that can record a recovery phrase. Go directly to the official MetaMask download page when choosing an installer.
The guide on metamaskwallet.to described network fees, swaps and self-custody. These were explanations of wallet functions. They supply no basis for attributing a brokerage account, deposit plan, fixed return or withdrawal policy to the domain operator. In particular, a discussion of a blockchain fee is insufficient evidence that this publisher charged anyone to release funds.
Who Published the Guide?
The sources reviewed did not establish who controlled metamaskwallet.to, what legal entity published the guide, or whether MetaMask authorized its use of the brand. The name on the page identifies the product discussed. Without a separate operator name, corporate identifier or jurisdiction tied to the site, a company-register search for the wallet brand could easily identify the wrong party.
The February capture gives a date by which the page was visible. It cannot establish when the publisher began operating, when it gained control of the address, or how long the same content remained online. We did not independently verify registry chronology, a business address, a financial licence or an operator response. No approach was made to a purported operator.
Frequently Asked Questions
Does the Screenshot Show a Recovery Phrase Request?
The visible portion shows a guide and navigation. There is no recovery phrase field in that view. Other routes, interactive elements and later versions are separate questions. The login route could not be retrieved for this review, so we cannot describe the form a visitor would have reached or where any information would have gone.
Is Visiting the Guide Evidence That My Wallet Was Drained?
A visit alone does not establish a transfer. If you are reconstructing an incident, distinguish opening a page from installing software, entering a secret, connecting a wallet or approving a transaction. A timestamped message, browser-history entry and public transaction hash each document a different part of that sequence. Keep recovery phrases and private keys out of any evidence you share.
Conclusion and Reporting Guidance
The archived guide and the exact-domain phishing classification warrant avoiding metamaskwallet.to for downloads, logins or wallet recovery. We leave the operator’s identity, current site behavior and any individual loss unscored. Readers can act on the documented warning without having to resolve those questions or revisit the address.
If you encountered metamaskwallet.to through a message or advertisement, retain the original link, date and screenshot. If funds moved, record the public transaction hash and network. InvestorWatchdog’s financial fraud reporting guide explains how to organize those records. To share evidence about this particular domain with the editorial team, use the tip submission form and redact wallet secrets.