Trading bot API keys connect software to an exchange account with permissions you choose. The important question is what that software can read, trade or withdraw. A bot’s promised strategy tells you little about the authority in the key. Inspect those permissions inside your own exchange account before sharing access.
Define the Job Before Creating Trading Bot API Keys
A portfolio tracker may need balances and transaction history to display holdings. A trading strategy may need to place and cancel orders. A tool that merely calculates returns has a different job again. Write down the intended task in one sentence before opening the permission settings.
Now compare every requested permission with that task. Ask the provider why it needs each one. A generic instruction to enable all permissions makes the connection easier for the provider but gives you less control over the account. Keep the explanation and the final configuration together in your records.
Kraken’s security guidance distinguishes access to account information from actions such as placing orders and making withdrawals. It also recommends minimum necessary permissions and removing unused keys. Treat that exchange-specific guidance as a starting point for reading the options on your own platform. Kraken’s API key security guidance.
The Difference Between Trading and Withdrawing
An automated strategy might need to buy and sell assets inside the account. That does not automatically explain why it needs to send assets out. Ask specifically about withdrawal access and any permission to add withdrawal addresses. Check whether those controls are separate on the exchange you use.
For trading bot API keys, a key limited to trading can still expose you to losses through unwanted or risky orders. Removing withdrawal access addresses one channel of risk. You must also assess the strategy, account allocation and controls on trading activity before connecting software to funds.
Kraken separately explains that address-management permission can change where funds are eligible to be sent, with additional implications when combined with withdrawal permission. Review combinations of permissions as well as individual switches. Read the withdrawal-address permission explanation.
An Illustrative Permission Review
Suppose a service says it will display your holdings and calculate returns. It then asks for order creation, withdrawals and an API secret. Ask it to explain why a reporting function needs the ability to move money. If it offers a read-only configuration, verify that selection yourself in the exchange settings.
A different service may genuinely execute a strategy. In that case, record which assets it can trade, what account or subaccount it accesses and how you can stop it. Avoid assuming that a spending limit in the bot’s own interface is enforced by the exchange. Identify where each restriction actually operates.
Keep the Key Out of Ordinary Messages
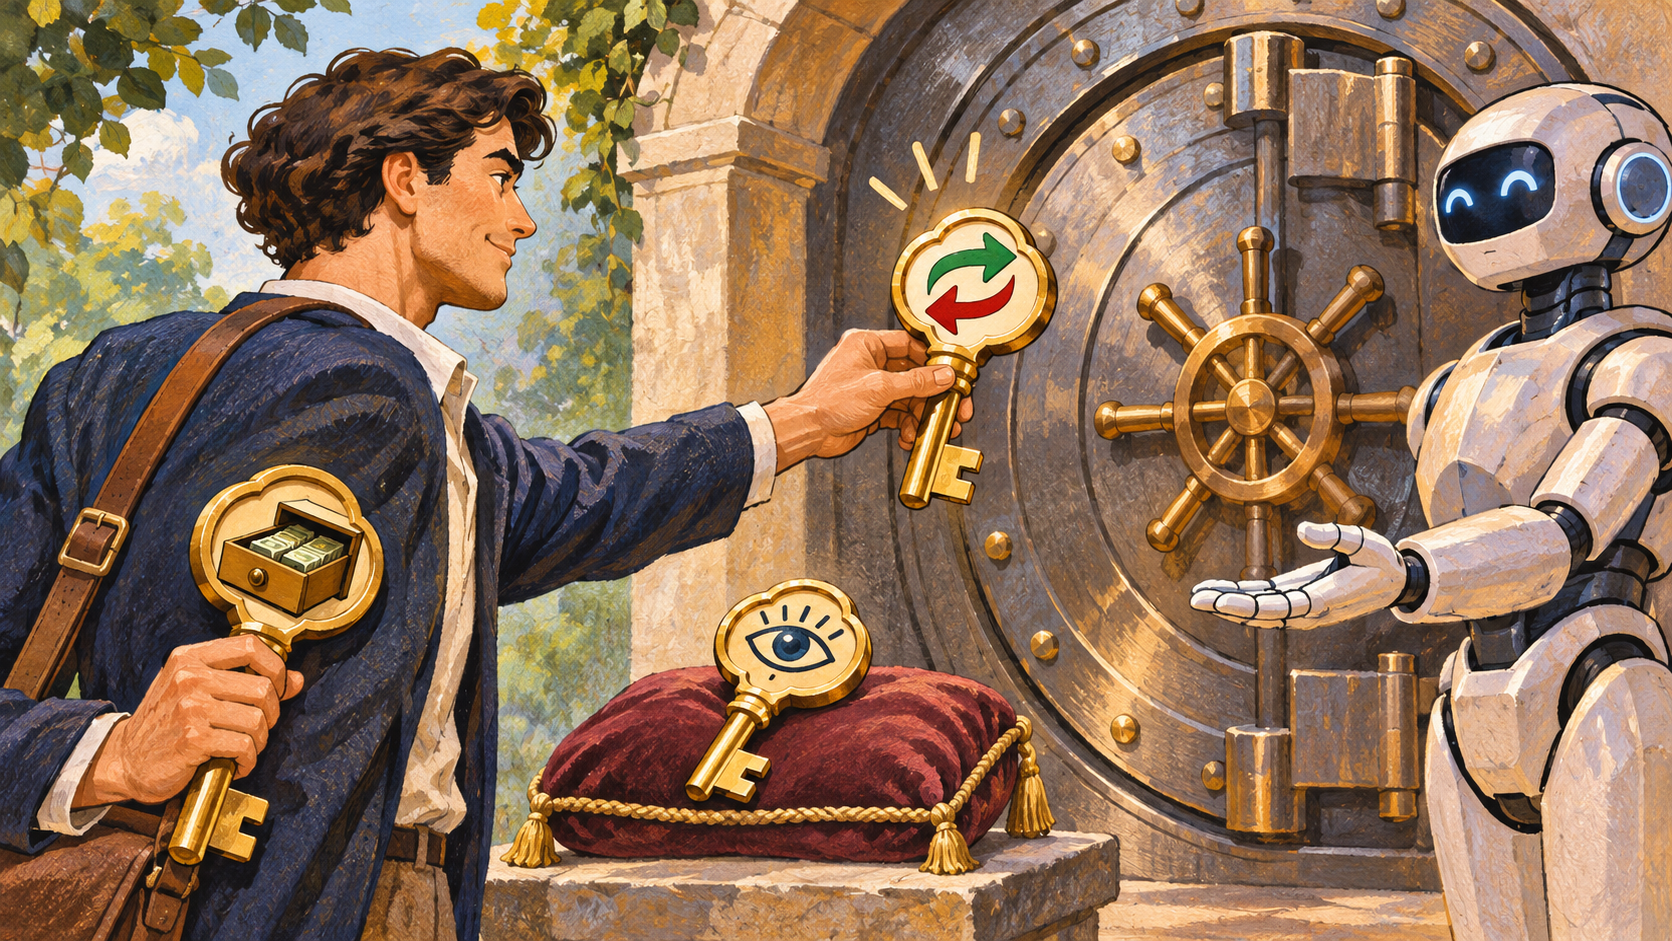
Treat the secret component as a credential. Avoid sending it through group chats, screenshots or support tickets. A QR code may encode sensitive access information too. Use the provider’s documented connection process only after checking its identity, and review how it says credentials are stored and protected.
Separate trading bot API keys by service where the exchange supports that approach. A dedicated key makes it easier to identify which integration generated activity and to revoke one connection without disrupting another. Name the key clearly enough that you can recognise its purpose months later.
Before and After Connecting
Save the selected permissions and creation date without exposing the secret. Start with the account scope appropriate to the task and check the first activity log entries. Compare them with what the software said it would do. Unexpected orders or permission changes deserve attention even if the account has yet to lose money.
The article on CryptoNest examines the distinction between trading claims and performance evidence. Use that analytical approach when a bot vendor supports its access request with a results chart. Read the CryptoNest performance review.
Review trading bot API keys periodically. Remove unused connections and follow the exchange’s process when rotating credentials. Confirm that revoking a key ends the integration’s access, then inspect open orders separately. Existing orders or positions may require additional action through the exchange.
If You Suspect Misuse
Use a trusted device and the exchange’s official interface to revoke the affected access promptly. Contact its security team, identify the key by its safe label or identifier and preserve relevant activity records. Explain which actions you recognise and which you dispute. Keep credentials out of the report.
Our crypto safety guide offers broader account-protection context for the steps surrounding an integration. It is especially relevant if the same third party also requested wallet access or remote control. Review crypto account safety.
When comparing trading bot API keys, also ask whether the exchange supports restrictions such as expiry or approved network addresses. Availability and behaviour vary, so use the exchange’s documentation for your account type. Record who will maintain those settings when the provider changes its infrastructure or when you stop using the service.
A Final Test for Trading Bot API Keys
You should be able to explain what the key permits, who receives it and how to revoke it. If those answers remain unclear, connecting the bot would put money behind an unanswered operational question. Resolve that question before relying on the promised returns.